Establishing Link...
SecureEncrypted
Sovereign Validator scans Terraform state (.tfstate) — the deployed reality, not the code — against ~102 OPA Rego rules in 24 policy namespaces covering DORA, GDPR and AMLD5, with regulator-ready xBRL-CSV and evidence exports. Live on AWS EKS; the public demo scans synthetic Terraform state.
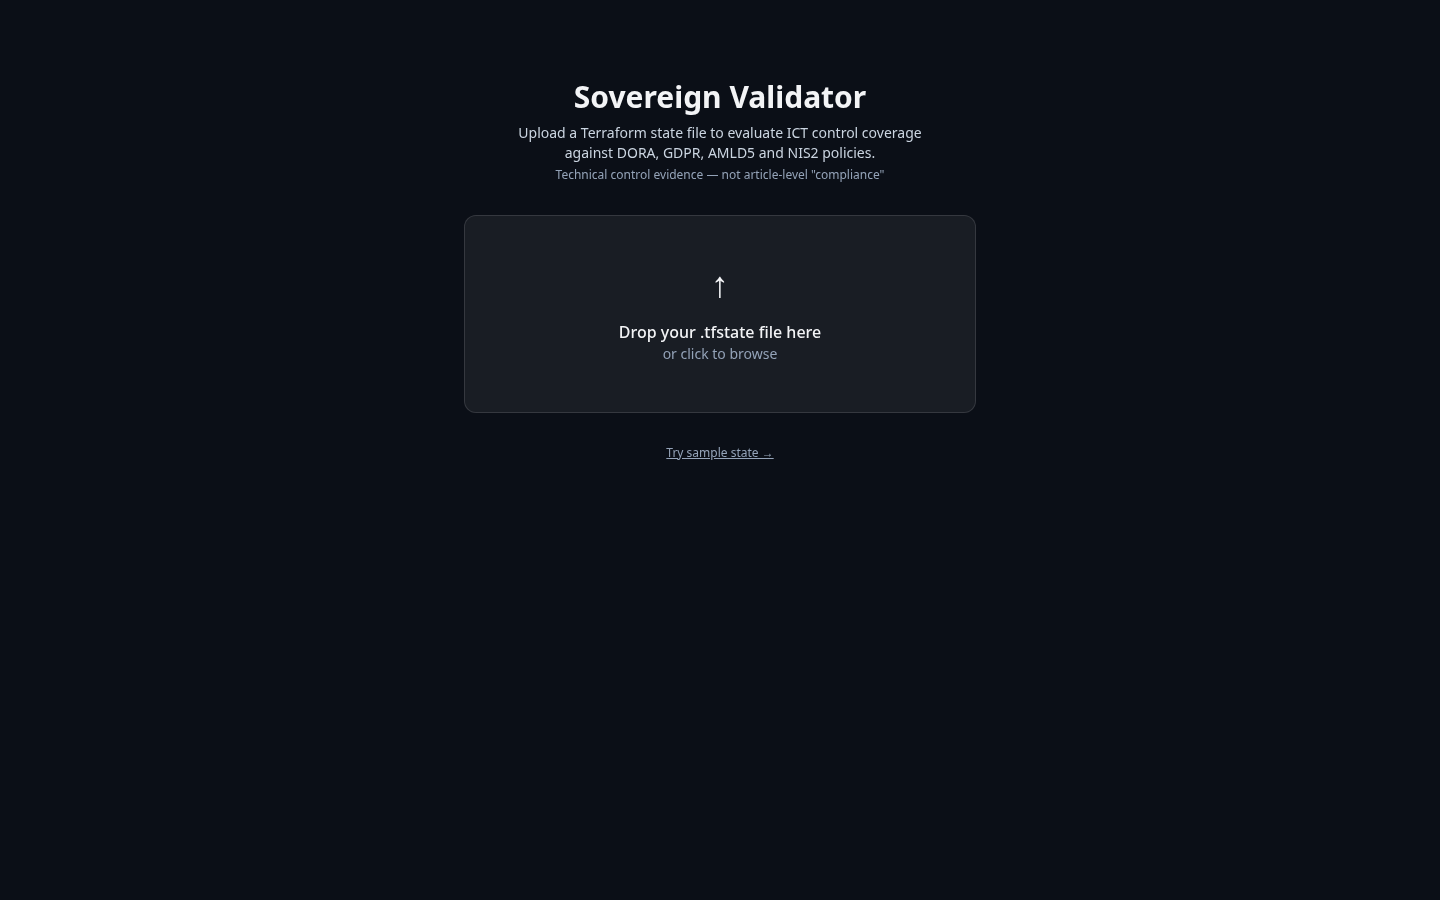
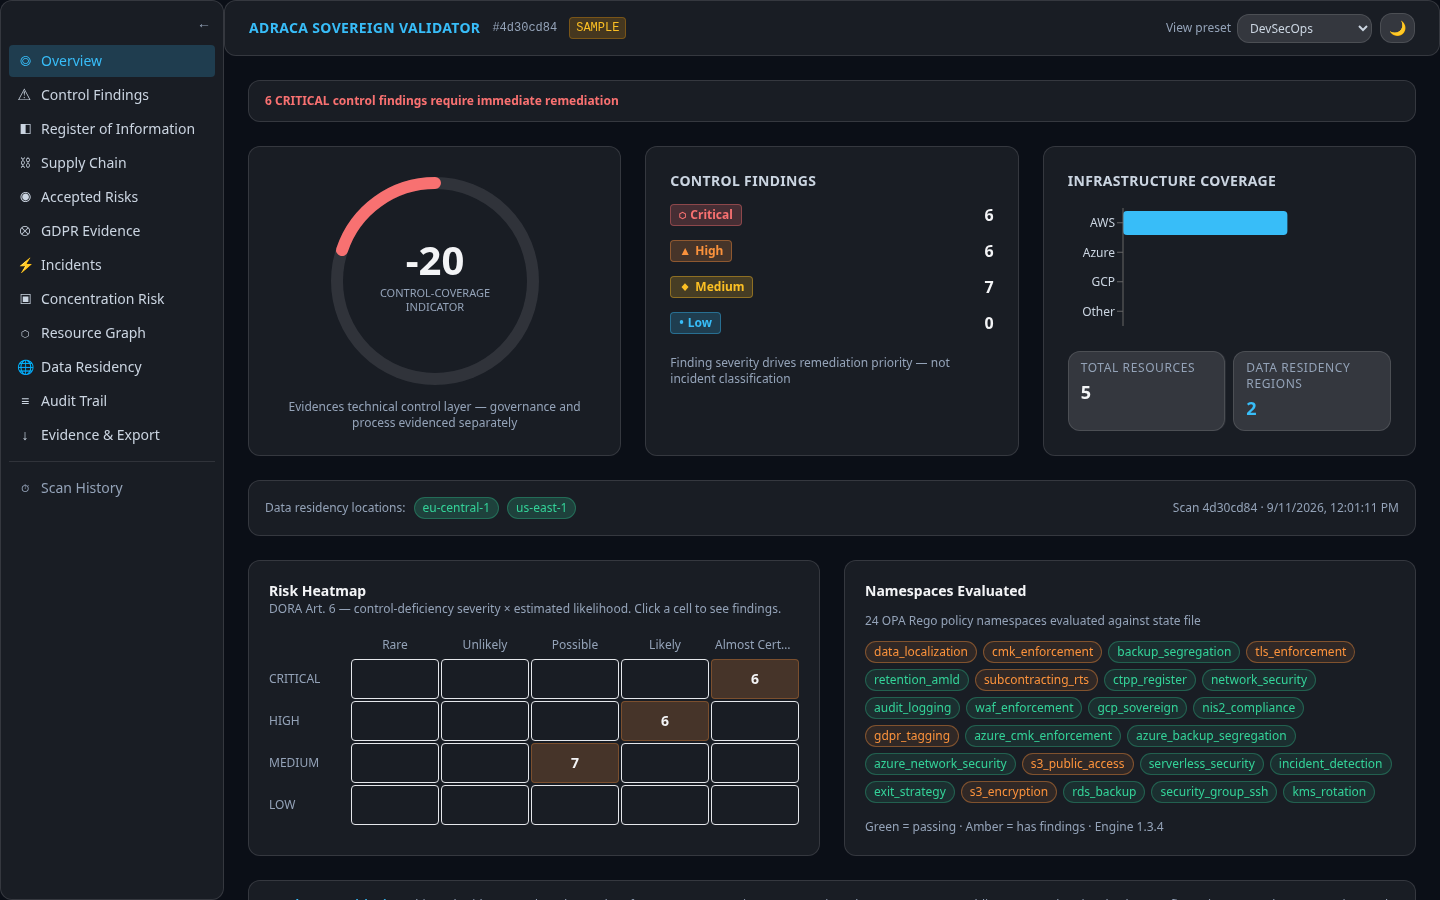
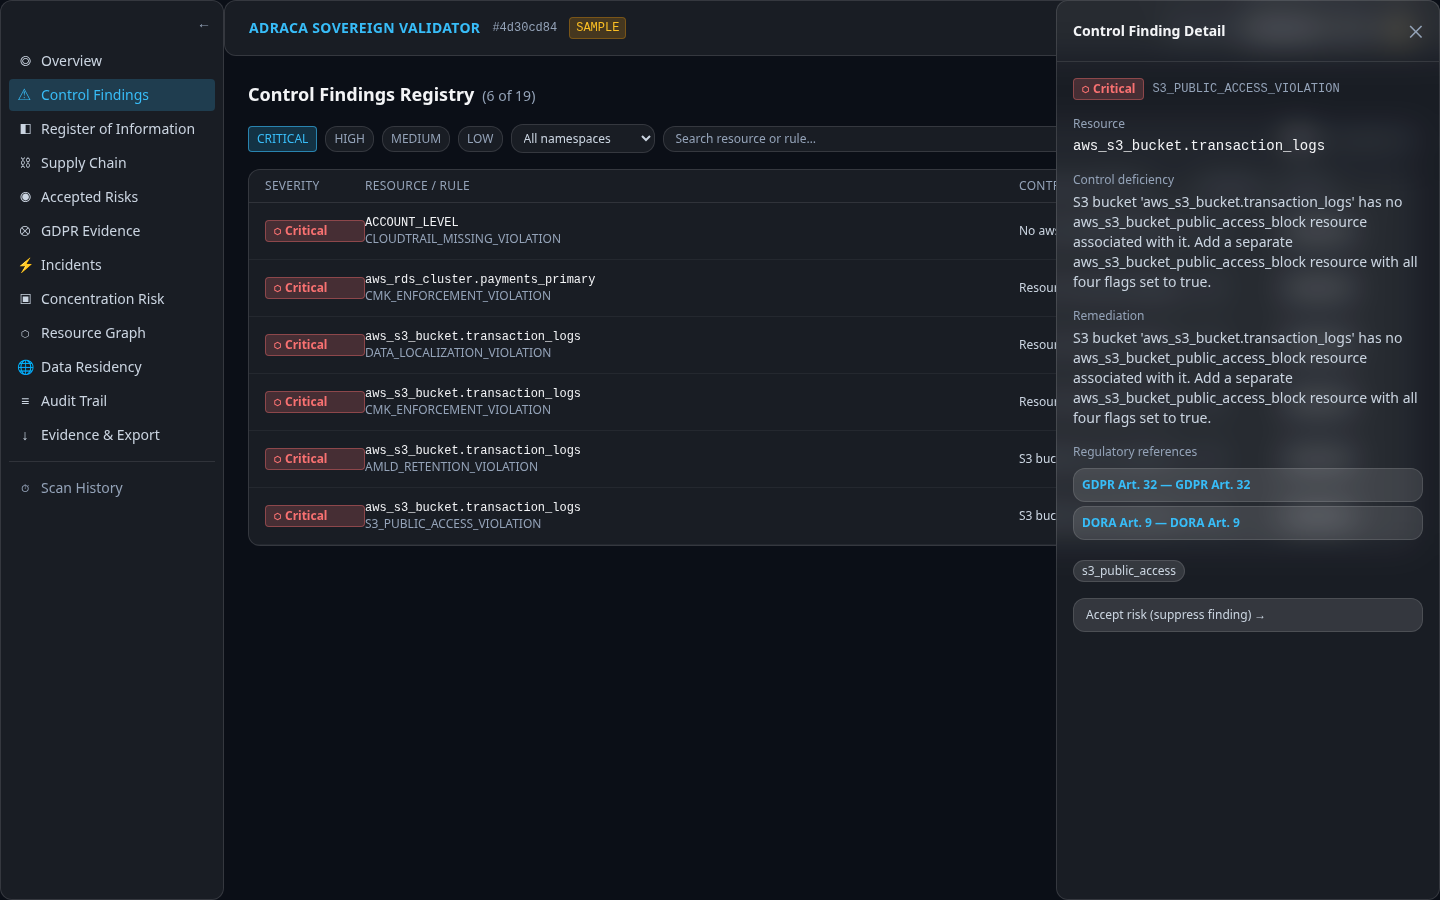
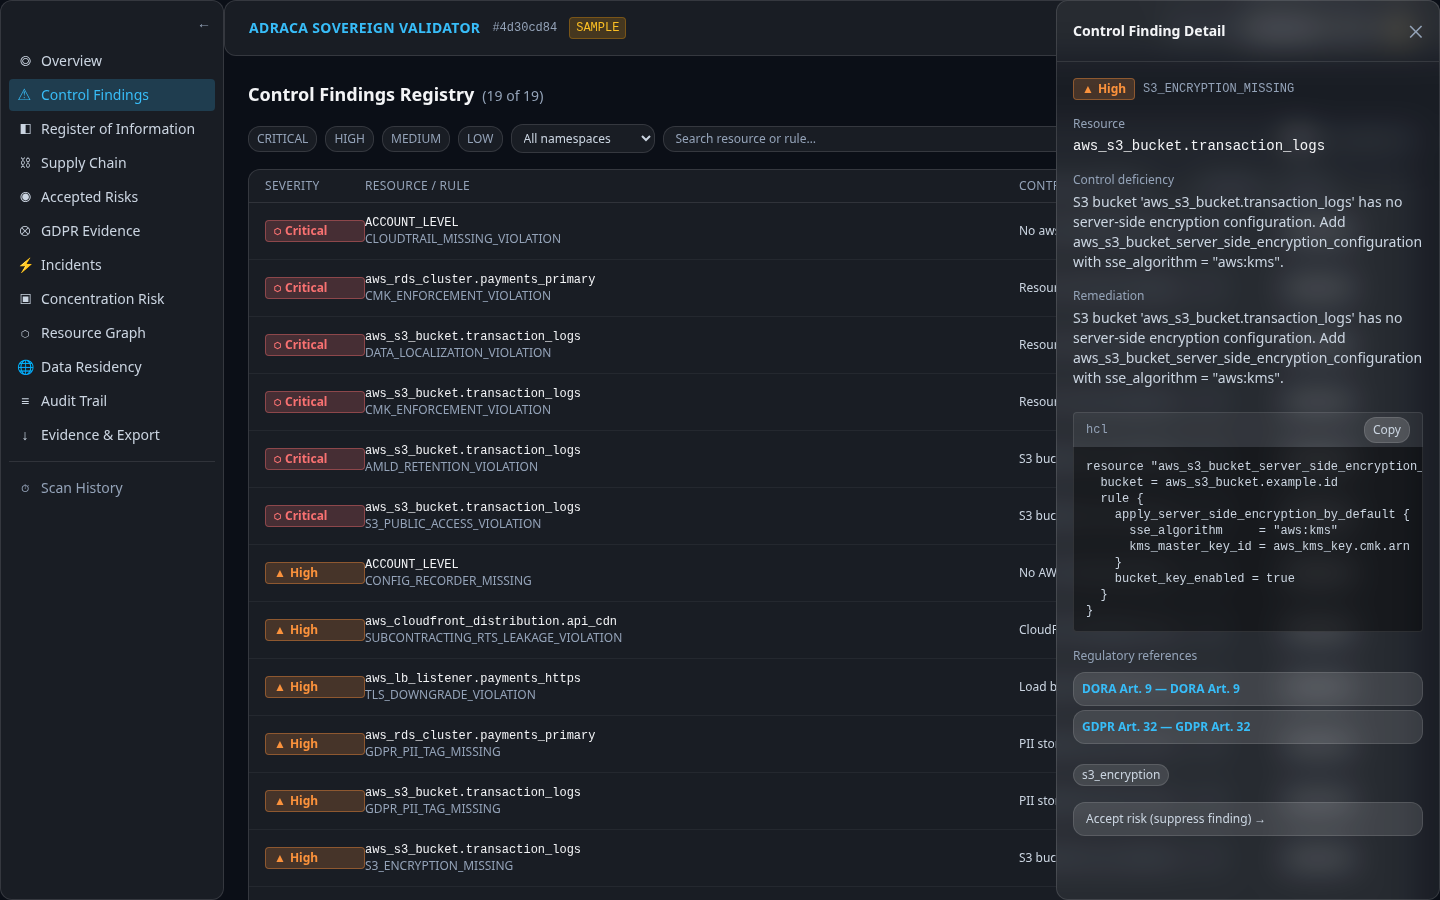
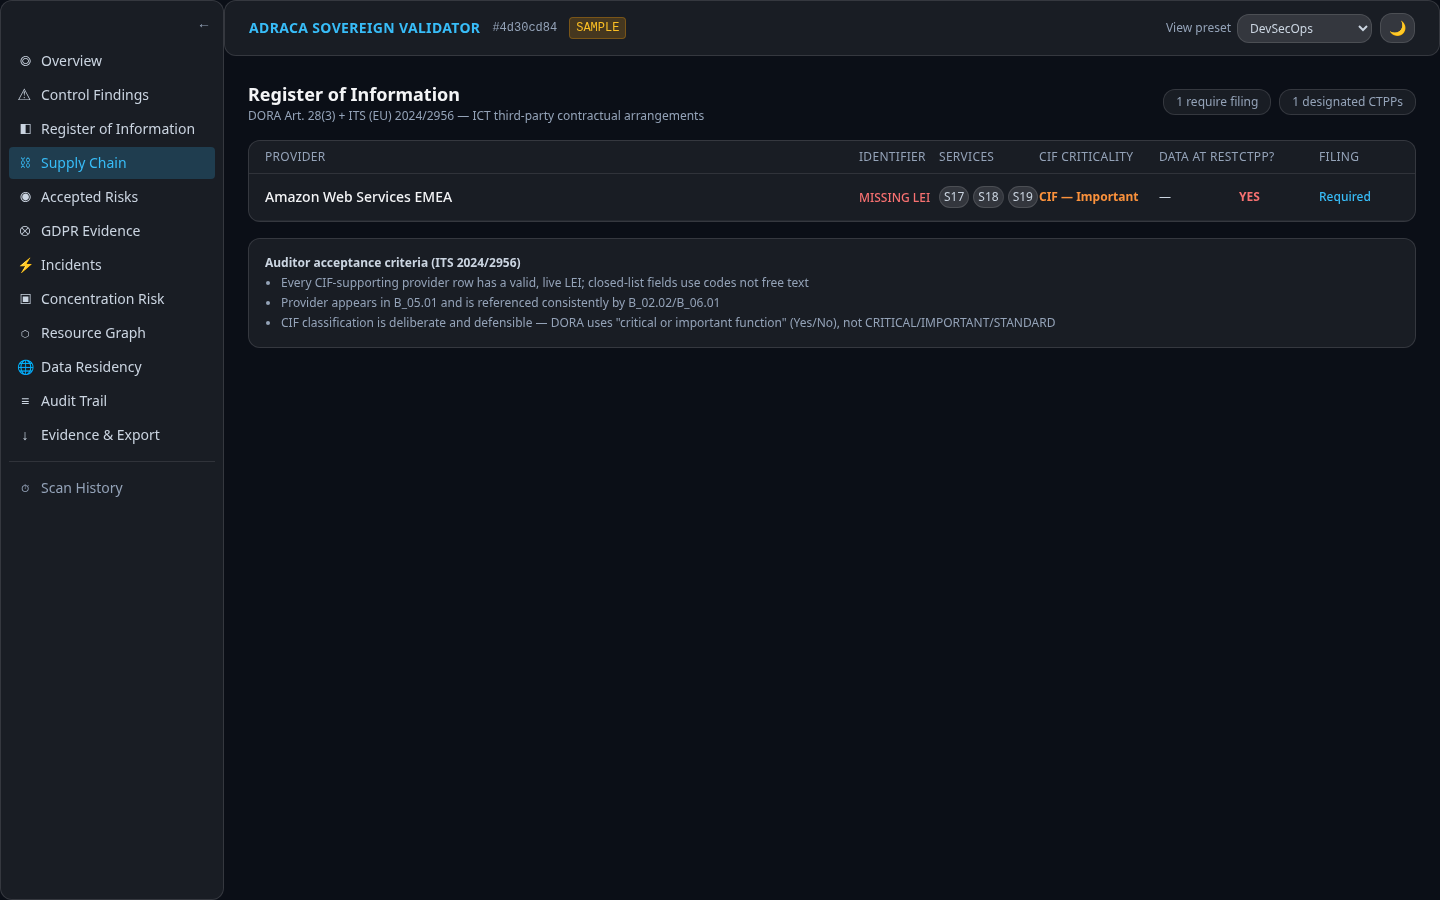
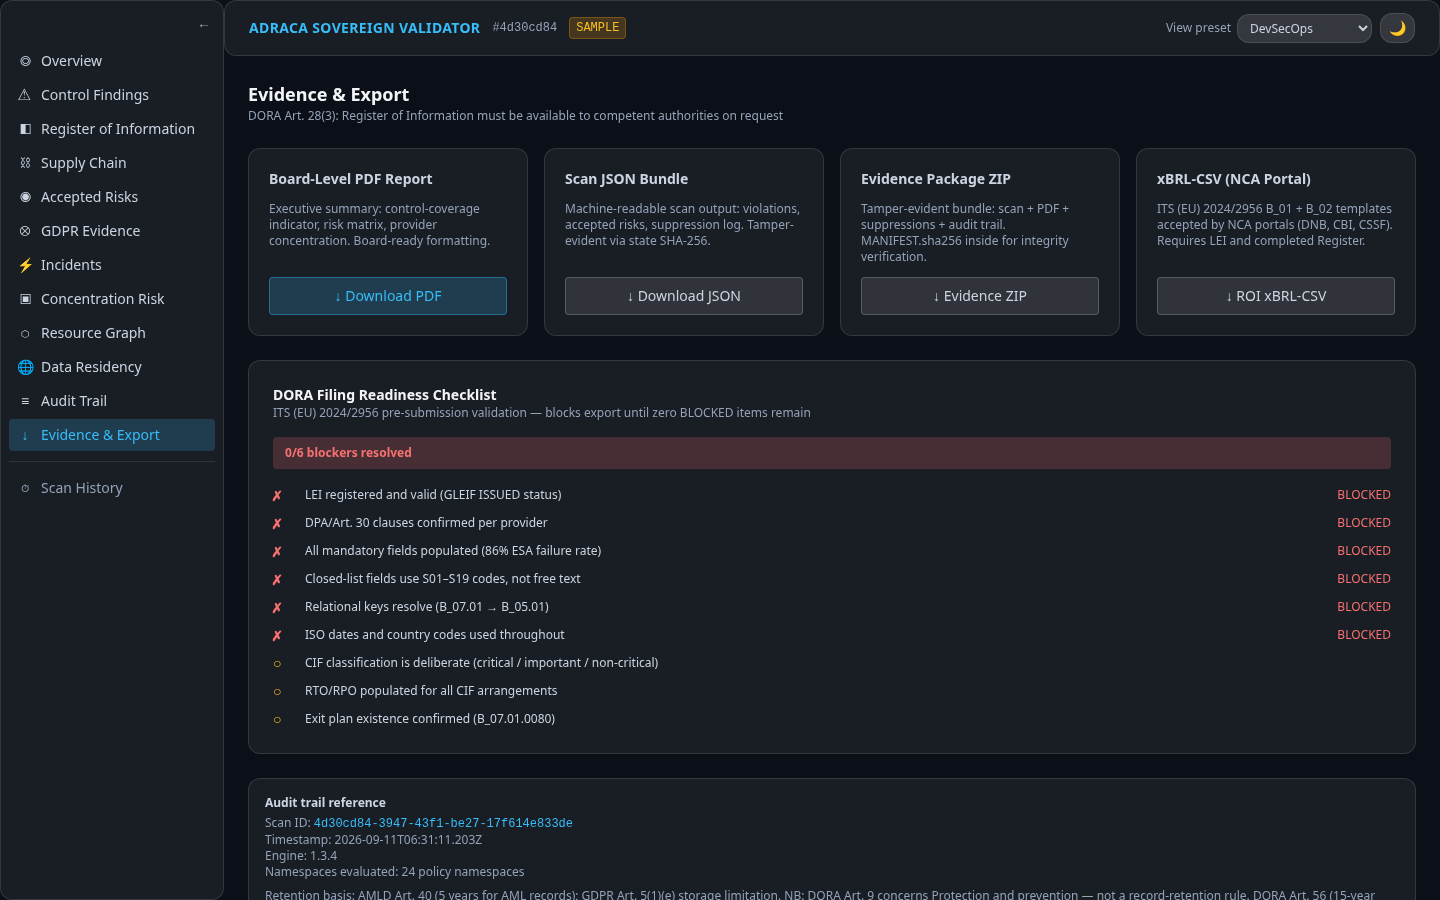
Parses .tfstate instead of HCL to inspect the ground truth of deployed infrastructure, with policy namespaces for AWS, Azure and GCP resources.
xBRL-CSV register-of-information export per ITS 2024/2956, plus an evidence ZIP with a SHA-256 manifest for every scan.
Classifies findings against the seven RTS 2024/1772 criteria with Zone A/B reporting countdown clocks (≤4 h / ≤24 h).
Implements Open Policy Agent (OPA) with Rego to evaluate declarative infrastructure compliance rules against JSON input contexts.
Recursive parser traversing module hierarchies inside Terraform state files to inspect the realized architecture instead of code.
Strips and HMAC-SHA256-hashes PII field values in the state file before any policy evaluation runs.
CTPP register (DORA Art. 28), xBRL-CSV ROI export, evidence ZIP with SHA-256 manifest, suppressions with audit trail.
Parses .tfstate and flattens recursive module hierarchies into evaluable resource records.
PII values stripped or HMAC-hashed so no personal data reaches the policy engine.
~102 rules across 24 namespaces — DORA, GDPR and AMLD5 policy sets — via OPA.
Violations with HCL remediation snippets; CTPP register, xBRL-CSV and evidence ZIP generated.